 By
The digital frontlines of Eastern Europe reached a critical threshold today when unauthorized threat actors breached primary mobile emergency alert applications operating in both Ukraine and Russia. By transmitting false push notifications warning of nuclear hazards and chemical contamination directly to millions of civilian devices, the cyber intrusions caused widespread momentary panic, compelling military command centers and civil defense authorities on both sides to rapidly issue counter-dispatches and restrict compromised communication channels.
Strategic Background & Timeline of the Dual Breach
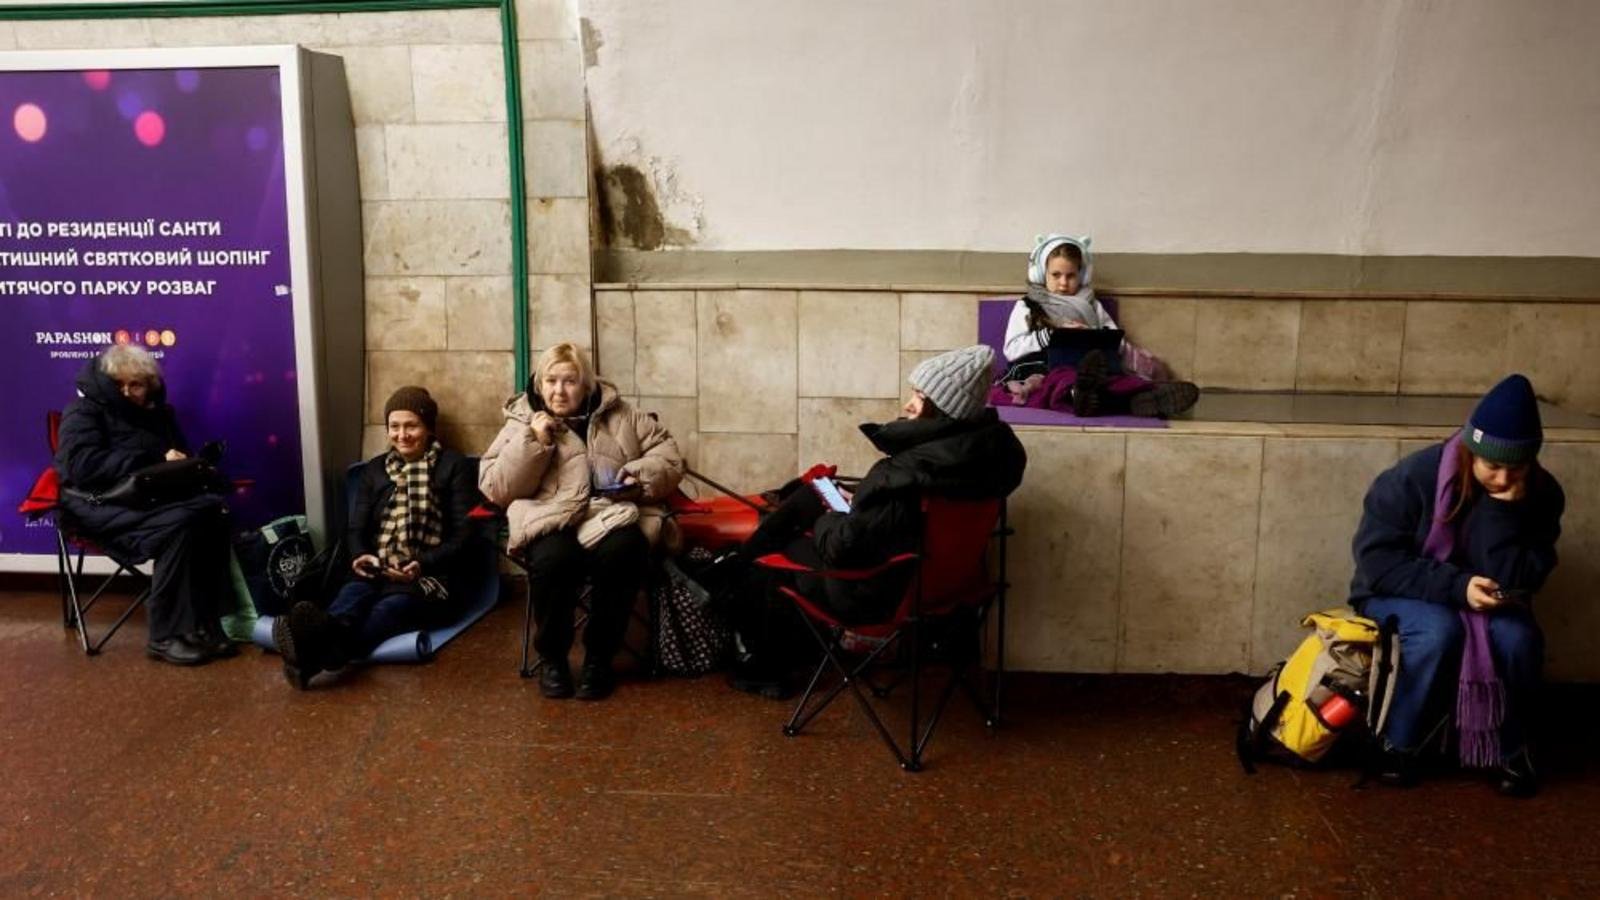
Civil defense applications have served as essential digital lifelines since the outbreak of kinetic hostilities, translating radar telemetry and air defense tracking into immediate, localized push notifications. Millions of residents rely entirely on these mobile architectures to seek shelter from incoming missile strikes, drone swarms, and artillery barrages. Today, however, that trust was severely tested when engineered vulnerabilities allowed malicious actors to hijack notification pipelines.
Early in the morning, users across multiple Ukrainian oblasts reported receiving unprecedented alert banners. Rather than standard notifications warning of conventional air raids or incoming ballistic threats, the compromised software warned of localized radiological fallout and urged immediate evacuation or chemical shelter protocols. Ukraine’s Air Force command released a swift clarification, acknowledging that the mobile alert application had experienced a sophisticated cyber intrusion and confirming that no radiation threats existed across national territory.
In a striking development hours later, official Russian state media and regional emergency services confirmed that internal Russian civil defense applications—alongside localized automated broadcast streams—had suffered a mirrored intrusion. Residents in western Russian regions received automated audio clips and push alerts falsely warning of pending nuclear strikes and environmental hazard zones. Russian digital security agencies immediately severed network connections to affected servers to halt the distribution of spoofed transmissions.
Technical Exploitation Vectors and Threat Analysis
While formal forensic attribution remains ongoing, cybersecurity analysts point to vulnerabilities within cloud-based push notification servers and compromised API credentials rather than direct intrusions into military radar networks. Modern mobile alert infrastructure relies heavily on intermediate content delivery networks and third-party push notification architecture to reach millions of endpoints within seconds. Accessing administrative tokens within these pipeline components allows threat actors to craft customized, authenticated alerts without overriding localized radar telemetry.
Independent threat intelligence firms monitoring the region suggest two primary operational possibilities: a synchronized dual-pronged attack executed by a sophisticated third-party threat group seeking total regional destabilization, or rapid retaliatory counter-strikes launched by opposing hacktivist collectives utilizing similar zero-day vulnerabilities discovered within commercial push notification software.
Compromising early-warning infrastructure shifts cyber operations from tactical data exfiltration to direct psychological warfare. When populations can no longer trust verified safety notifications during active conflict, the fundamental mechanism of civil defense begins to erode.
Psychological Operations and the Weaponization of Radiological Fear
The deliberate selection of radiation warnings underscores a calculated strategy aimed at amplifying public alarm. Given Eastern Europe’s historical sensitivity to nuclear incidents and ongoing kinetic activity near nuclear power facilities like Zaporizhzhia, alerts referencing radiological hazards trigger immediate mass anxiety. By inserting false environmental hazards into trusted civil notification streams, threat actors aim to induce civil paralysis, overwhelm emergency call centers, and generate traffic gridlock near major urban hubs.
Psychological warfare experts note that weaponizing emergency alert systems poses systemic risks far beyond initial false alarms. Repeated compromises risk creating alert fatigue or skepticism among the civilian populace. If citizens begin questioning the authenticity of air raid sirens or mobile notifications, life-saving response times during actual kinetic strikes could be catastrophically delayed.
Key Takeaways & Strategic Intelligence
- Bypassing Military Targets: Cyber adversaries are increasingly targeting civilian safety networks rather than hardened military command servers to achieve maximum societal disruption.
- Weaponized Nuclear Panic: The deployment of false radiological alerts leverages deep regional anxieties to induce civil congestion and paralyze localized emergency management networks.
- Supply Chain Vulnerabilities: Compromised push notification APIs highlight systemic security gaps within third-party mobile distribution infrastructure.
- Erosion of Digital Trust: Recurring intrusions threaten public compliance with verified emergency protocols, creating long-term risks during genuine kinetic combat.
Geopolitical Implications and Infrastructure Resilience
The simultaneous disruption of civilian safety networks in both Ukraine and Russia marks a significant turning point in global cyber warfare conventions. International observers from NATO cyber defense centers and European cybersecurity agencies are closely evaluating the incidents, warning that critical national infrastructure protocols must now treat civil defense mobile apps with the same baseline defensive priority as power grids and water filtration facilities.
Government ministries in Kyiv and Moscow have initiated security audits of all public warning software, temporarily mandating secondary verification protocols before emergency broadcasts can be cleared for distribution. Security engineers are currently rotating API access keys, isolating distribution nodes, and working alongside global tech conglomerates to patch credential leaks that enabled the malicious push sequences.
Future Outlook & Strategic Projections
In the coming months, emergency management agencies globally are expected to re-architect digital civil defense systems. Defense analysts project a transition toward decentralized notification systems anchored by cryptographic verification tokens, ensuring that individual mobile devices can authenticate the cryptographic signature of any state-issued alert before displaying high-priority warning banners to end users. Without robust cryptographic verification, public warning systems will remain vulnerable to hybrid warfare techniques designed to sow panic across civilian populations.