

 By
Pakistan’s National Cyber Emergency Response Team has issued an urgent advisory warning organizations about a high-severity vulnerability in TeamViewer. The flaw, tracked as CVE-2026-111585, carries a CVSS score of 8.8 out of 10. It affects TeamViewer clients running versions earlier than 15.83 across Windows, Linux, and macOS. If exploited, the vulnerability could let attackers crash systems or execute malicious code remotely.
The flaw sits in the component that processes remote-control screen data. An integer overflow in that component can trigger memory corruption under specific conditions. For exploitation to work, the victim needs to connect to a remote-control session hosted by an attacker-controlled or compromised machine. That requirement makes organizations relying on remote technical support, system administration, and external IT connections the most relevant targets.
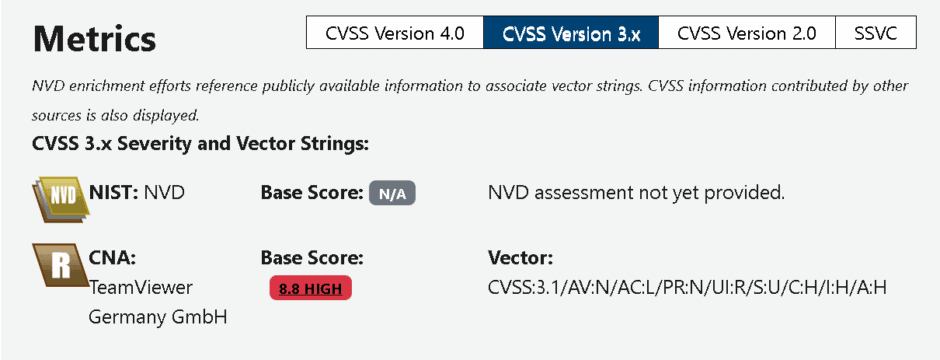
NCERT stressed that the consequences extend beyond individual machines. In environments where remote-access software manages critical systems, a single exploited session could compromise entire networks. Successful exploitation threatens the confidentiality, integrity, and availability of affected endpoints. The level of damage depends on system configuration and the privileges available to the compromised process.
The affected software includes TeamViewer Full Client and TeamViewer Portable for Windows, along with clients for Linux, macOS, and certain Android remote-control applications. Legacy branches are also vulnerable. Organizations running older 14.x releases should update to version 14.7.48868. Those on 13.x releases need version 13.2.36231. Everyone else should upgrade to version 15.83 or later immediately.
What is affected
| CVE | CVSS 3.1 | What it allows | Affected | Fixed in |
|---|---|---|---|---|
| CVE-2026-111585 | 8.8 High | A malicious or compromised remote host crashes the connecting viewer and, depending on the platform, runs code with the viewer’s privileges | TeamViewer Full Client and Portable before 15.83 (Windows, Linux, macOS); Remote Control app for Android before 15.83 | 15.83 |
| CVE-2026-92372 | 8.8 High | Code execution through crafted screen data in a session, or by opening a crafted session recording (.tvs) |
TeamViewer Full Client and Host before 15.83 on Linux and macOS | 15.83 |
| CVE-2026-92374 | 7.8 High | A local user with low privileges gains root on macOS through the TeamViewer privileged helper | TeamViewer Full Client and Host before 15.83 on macOS | 15.83 |
For organizations that cannot patch right away, NCERT recommended blocking untrusted outbound remote connections and restricting exposure of vulnerable systems until updates are applied. The agency also advised restricting incoming and outgoing connections to approved IP addresses, authorized users, and trusted devices only. Unattended remote-access settings, authentication controls, and user permissions should all be reviewed. Administrative privileges should be limited to situations where they are operationally necessary.
NCERT further advised monitoring TeamViewer connection records, authentication events, and endpoint security alerts. Warning signs include unusual remote sessions, repeated software crashes, unexpected process activity, and unauthorized connections. However, the agency clarified that these indicators do not automatically confirm exploitation. They should be investigated alongside other available security data.
If compromise is suspected, organizations should assess affected devices and remote-session histories. Remote access should be restricted or disabled where necessary. Security logs should be preserved for investigation. Specialist incident-response assistance may be needed if arbitrary code execution or broader endpoint compromise appears likely.
The advisory references TeamViewer’s own Security Bulletin TV-2026-1011 and a corresponding advisory from the Canadian Centre for Cyber Security. For Pakistan, where remote access tools are widely used across corporate IT departments, managed service providers, and freelance technical support, the vulnerability carries particular relevance.
https://www.techjuice.pk/pakistan-ncert-teamviewer-vulnerability-advisory-remote-code-execution/


